JuanMa JWT Auth Pro
Active Installs
0+
Last Updated
December 11, 2025
First Released
December 11, 2025
Download History (Last one month)
Contributors
Unlike basic JWT plugins that use single long-lived tokens, JWT Auth Pro implements modern OAuth 2.0 security best practices with short-lived access tokens and secure refresh tokens.
Why JWT Auth Pro?
The Problem with Basic JWT Plugins:
* Long-lived tokens (24h+) = Higher security risk
* No refresh mechanism = Tokens live until expiry
* XSS vulnerable = Tokens stored in localStorage
* No revocation = Can’t invalidate compromised tokens
JWT Auth Pro Solution:
* Short-lived access tokens (1h default) = Minimal attack window
* Secure refresh tokens = HTTP-only cookies, XSS protected
* Automatic token rotation = Fresh tokens on each refresh
* Complete session control = Revoke any user session instantly
Features
- Simple JWT Authentication – Clean, stateless token-based auth
- HTTPOnly Refresh Tokens – Secure refresh tokens in HTTP-only cookies
- Token Rotation – Automatic refresh token rotation for enhanced security
- CORS Support – Proper cross-origin request handling
- Clean Admin Interface – Simple configuration in WordPress admin
- Developer Friendly – Clear endpoints and documentation
Security Comparison
Feature
Basic JWT Plugins
JWT Auth Pro
Token Lifetime
Long (hours/days)
Short (1 hour)
Refresh Tokens
None
Secure HTTP-only
XSS Protection
Limited
HTTP-only cookies
Token Revocation
Manual only
Automatic rotation
Session Management
None
Database tracking
Security Metadata
None
IP + User Agent
Perfect for:
- Single Page Applications (React, Vue, Angular)
- Mobile Applications (iOS, Android)
- API Integrations (Third-party services)
- Headless WordPress (Decoupled architecture)
API Endpoints
POST /wp-json/jwt/v1/token– Login and get access tokenPOST /wp-json/jwt/v1/refresh– Refresh access tokenGET /wp-json/jwt/v1/verify– Verify token and get user infoPOST /wp-json/jwt/v1/logout– Logout and revoke refresh token
Security
- Stateless Authentication – JWT tokens contain all necessary information
- HTTPOnly Cookies – Refresh tokens stored securely, inaccessible to JavaScript
- Token Rotation – Refresh tokens automatically rotate on use
- Configurable Expiration – Set custom expiration times
- IP & User Agent Tracking – Additional security metadata
Support
For support and documentation, visit: https://github.com/juanma-wp/jwt-auth-pro-wp-rest-api
Privacy Policy
This plugin stores user session data including IP addresses and user agent strings for security purposes. This data is used solely for authentication and security monitoring.
- Upload the plugin files to
/wp-content/plugins/directory - Activate the plugin through the ‘Plugins’ screen in WordPress
- Go to Settings JWT Auth Pro to configure the plugin
Configuration
Via wp-config.php (Recommended for production):
php

define('JWT_AUTH_PRO_SECRET', 'your-super-secret-key-here');

define('JWT_AUTH_PRO_ACCESS_TTL', 3600);      // 1 hour

define('JWT_AUTH_PRO_REFRESH_TTL', 2592000);  // 30 days
Via WordPress Admin:
Go to Settings JWT Auth Pro to configure:
* JWT Secret Key
* Token expiration times
* CORS allowed origins
* Debug logging
Screenshot Gallery


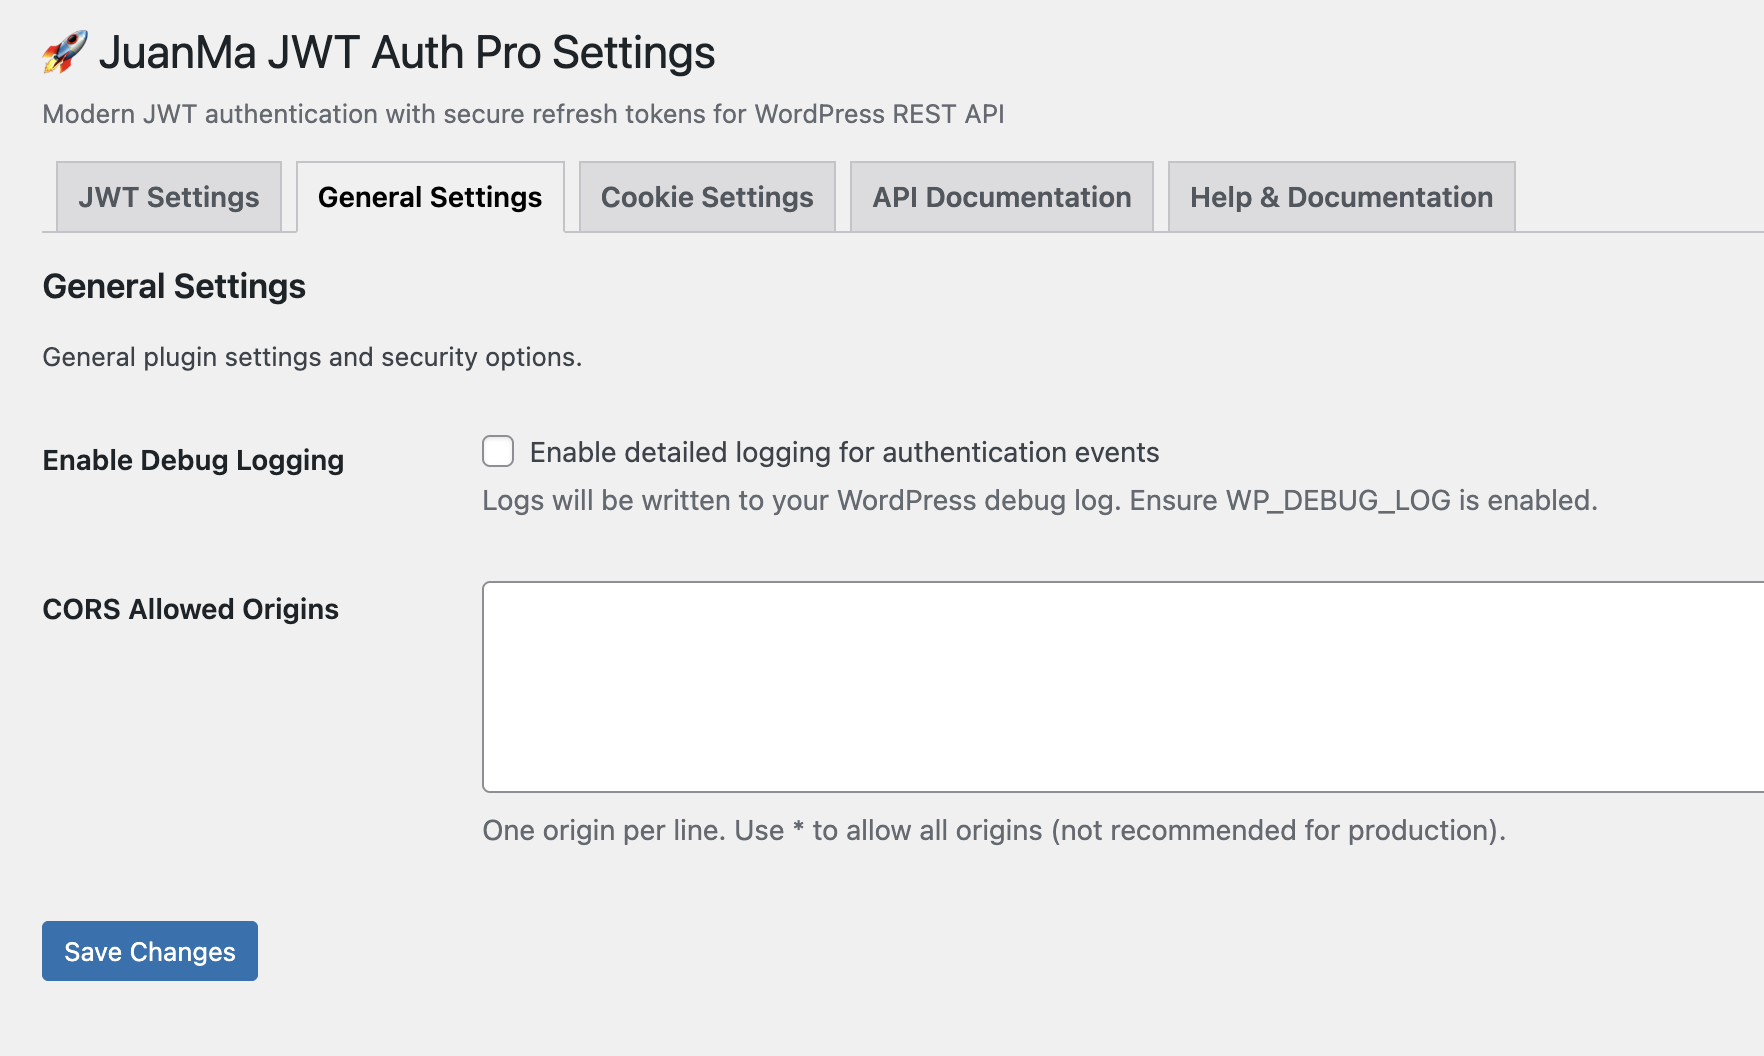
JWT Auth Pro implements modern security best practices with short-lived access tokens and secure refresh tokens, unlike basic JWT plugins that use long-lived tokens vulnerable to XSS attacks.
HTTPS is strongly recommended for HTTPOnly cookies to work securely, especially in production environments.
Yes! JWT Auth Pro is designed specifically for modern applications including mobile apps, SPAs, and API integrations.
You can revoke individual user sessions through the admin interface or programmatically using the provided API endpoints.
Changelog
1.0.0
- Initial release
- JWT authentication with access and refresh tokens
- HTTPOnly cookie support for secure refresh tokens
- Automatic token rotation
- CORS configuration
- Admin interface for plugin configuration
- Database session tracking
- IP and User Agent metadata for enhanced security
